Agentic traffic is up — and worth adapting to. At the same time, scams are tricking regular customers to use stolen cards in their own accounts.
The nature of accounts is changing. Accounts now have an extra possible stream of activity and transactions — agents — but are under more fraud pressure than ever as a vehicle for malicious activity.
The Fraud Temperature Gauge is tracking the month by month evolution of fraud at the speed of AI, drawing on and adding more context to the constantly updating data from https://intelligence.forter.com/.
September’s top eCommerce fraud trends: More agentic traffic and customers poisoning their own accounts
The two leading stories this month almost feel like they’re pulling in opposite directions.
Agentic transactions are increasing day-by-day. We’ve also seen a 107% growth in AI referral activity globally in September. This is supported by Forter research that found that 53% of UK shoppers have or are open to using AI to find Christmas gifts, with 22% believing AI would choose a better gift than their partner.
Agentic shopping sessions often aggregate bulk or subscription-style orders, such as with office supplies, pet supplies, or hygiene and wellness goods. This is itself an interesting angle on some of the use cases that are drawing early adopters to use AI in the first place.
The result of this tendency is that agentic orders have a higher AOV: $154 vs. $121 for humans.
As agentic traffic increases, fraudsters are putting a modern twist on an old scam. Scammers post on social media, and messaging groups and channels, offering a sizable discount (often as much as 50% off) at a particular retailer. They often pose as employees.
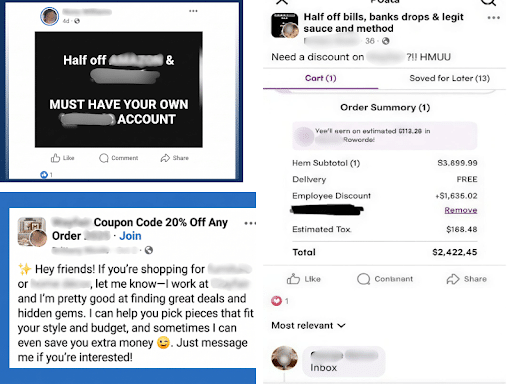
People message the scammer privately specifying the item/s they want, paying around 50% upfront and sharing their own account credentials. The fraudster makes the purchase with stolen credit card information from the customer’s real account — which has a legitimate shopping history.
This is similar to refund-as-a-service, in which real customers team up with fraudsters and agree to pay a fraction of what the goods are worth. In both cases, the consumers know that they’re cheating the system, but don’t usually realize that what they’re doing is serious abuse. Retailers know differently.
2.4 million attacks in September, 87% of which were perpetuated by coordinated fraud rings
It doesn’t make sense to chase fraudsters down one by one. With this level of coordination, bad actors have to be identified as part of the group threat that they typically are.
3.6K large, coordinated fraud rings detected across the network
Fraud ring traffic is more dominant during the weekends, with legitimate traffic taking a larger share of the whole during weekdays.
Account takeover attacks in Japan have doubled YoY
At the same time, third-party credit card fraud attacks have reduced by around 40%. This makes sense in the context of the introduction of 3DS in Japan; third-party credit card fraud is now more difficult, so fraudsters have shifted to Account Takeover instead. They don’t stop. They look for a different way forward.
Speaking of 3DS, Forter research indicates that merchants need to be careful not to send only high-risk traffic to 3DS. Sending a mix of traffic can lead to a 14% increase in authorization rate if done right. Different banks have different approaches to 3DS in what they want to see, so make sure you’re taking the right track with each one.
71% of attacks against digital goods came from IP addresses purportedly based in the US
This is tied to the popularity of US-based sites as targets for digital goods attacks. However, obfuscation is common with IP addresses as fraudsters try to hide their true location. Roughly half of the attacks of this type come in reality from Southeast Asia, and another ~30% are from Eastern Europe.
Ecommerce fraud trends by vertical
Ticketing surges in the summer, when many events are held. Forter data shows that when it comes to trying to steal tickets, attacks increased substantially against tickets on the day of the event — up to nearly 600% more than in the days or weeks leading up to it.
Fraudsters use automated credential stuffing tools like OpenBullet, SilverBullet, or Sentry MBA, loaded with custom configuration scripts (“configs”) tailored to a specific brand’s login API. When a valid login occurs, these tools execute data scraping directives and telemetry directly from the HTTP response payload. The fraudsters then sort the results by points, so accounts with high point balances or elite tiers are prioritized for immediate redemption or premium resale, while zero-balance accounts are discarded or sold in bulk batches.
ATO attacks against accounts with food and beverage, and QSR sites and apps have increased at least 20% every year for the last three years. Accounts with funds stored in them are 6.5x more likely to be targeted, mostly by repeat offenders. More than 85% of fraudsters trying fraud or abuse on QSR sites or apps have been there before.
During beauty merchants‘ promotions, up to 60% of declines for related orders to be due to promo abuse. It’s common for customers to pretend the product arrived broken, so they can keep their makeup and their money.
Fraud Ring Deep Dive: The Transatlantic Tricksters
Every month there’s a fraud ring that encapsulates key trends we’re seeing across multiple rings and bad actors. This month, it’s the Transatlantic Tricksters who have zeroed in on PayPal.
The majority of fraudster IPs originated from the UK, while two-thirds of bookings were concentrated on a single Asia-North America route that typically costs $3,500 per ticket. They largely used PayPal, with 34% showing failed attempts with other payments first.
The stats:
- 104 transactions
- 70 attempts in a single day
- $148,342.65 attempted (and blocked)
The Transatlantic Tricksters were full of red flags. In addition to the repeated retry pattern, and clear mismatch between their locations and flight itineraries, 79% of their accounts were brand new. They also displayed burst activity, with multiple rapid booking attempts within minutes, using different accounts from a shared IP range.
With a travel story, geographical diversity isn’t always a danger sign. But when it’s combined with a failed payment and a brand new account, things start to look more suspicious. Once a few of these can be connected to show ring activity, it’s time to flag and block the attack as a coordinated fraud ring attempt.
Get real-time fraud data
This month’s ecommerce fraud trends are a snapshot. The fraud landscape moves faster than any monthly recap can capture. For a real-time view of attacks blocked, ATO patterns, and fraud trends across industries and regions, explore Forter’s Fraud & Abuse dashboard.
You can filter by vertical or region to see what’s happening right now, and sign up for reports and alerts to stay ahead of the next Chrome Soles before it hits your site.